Built for your question · 3 sections from 1 page + 3 from the docs

Back to original
1 · From Hourglass for enterprises (opens in a new tab)
Hourglass for enterprises
Power for many teams, without the complexity

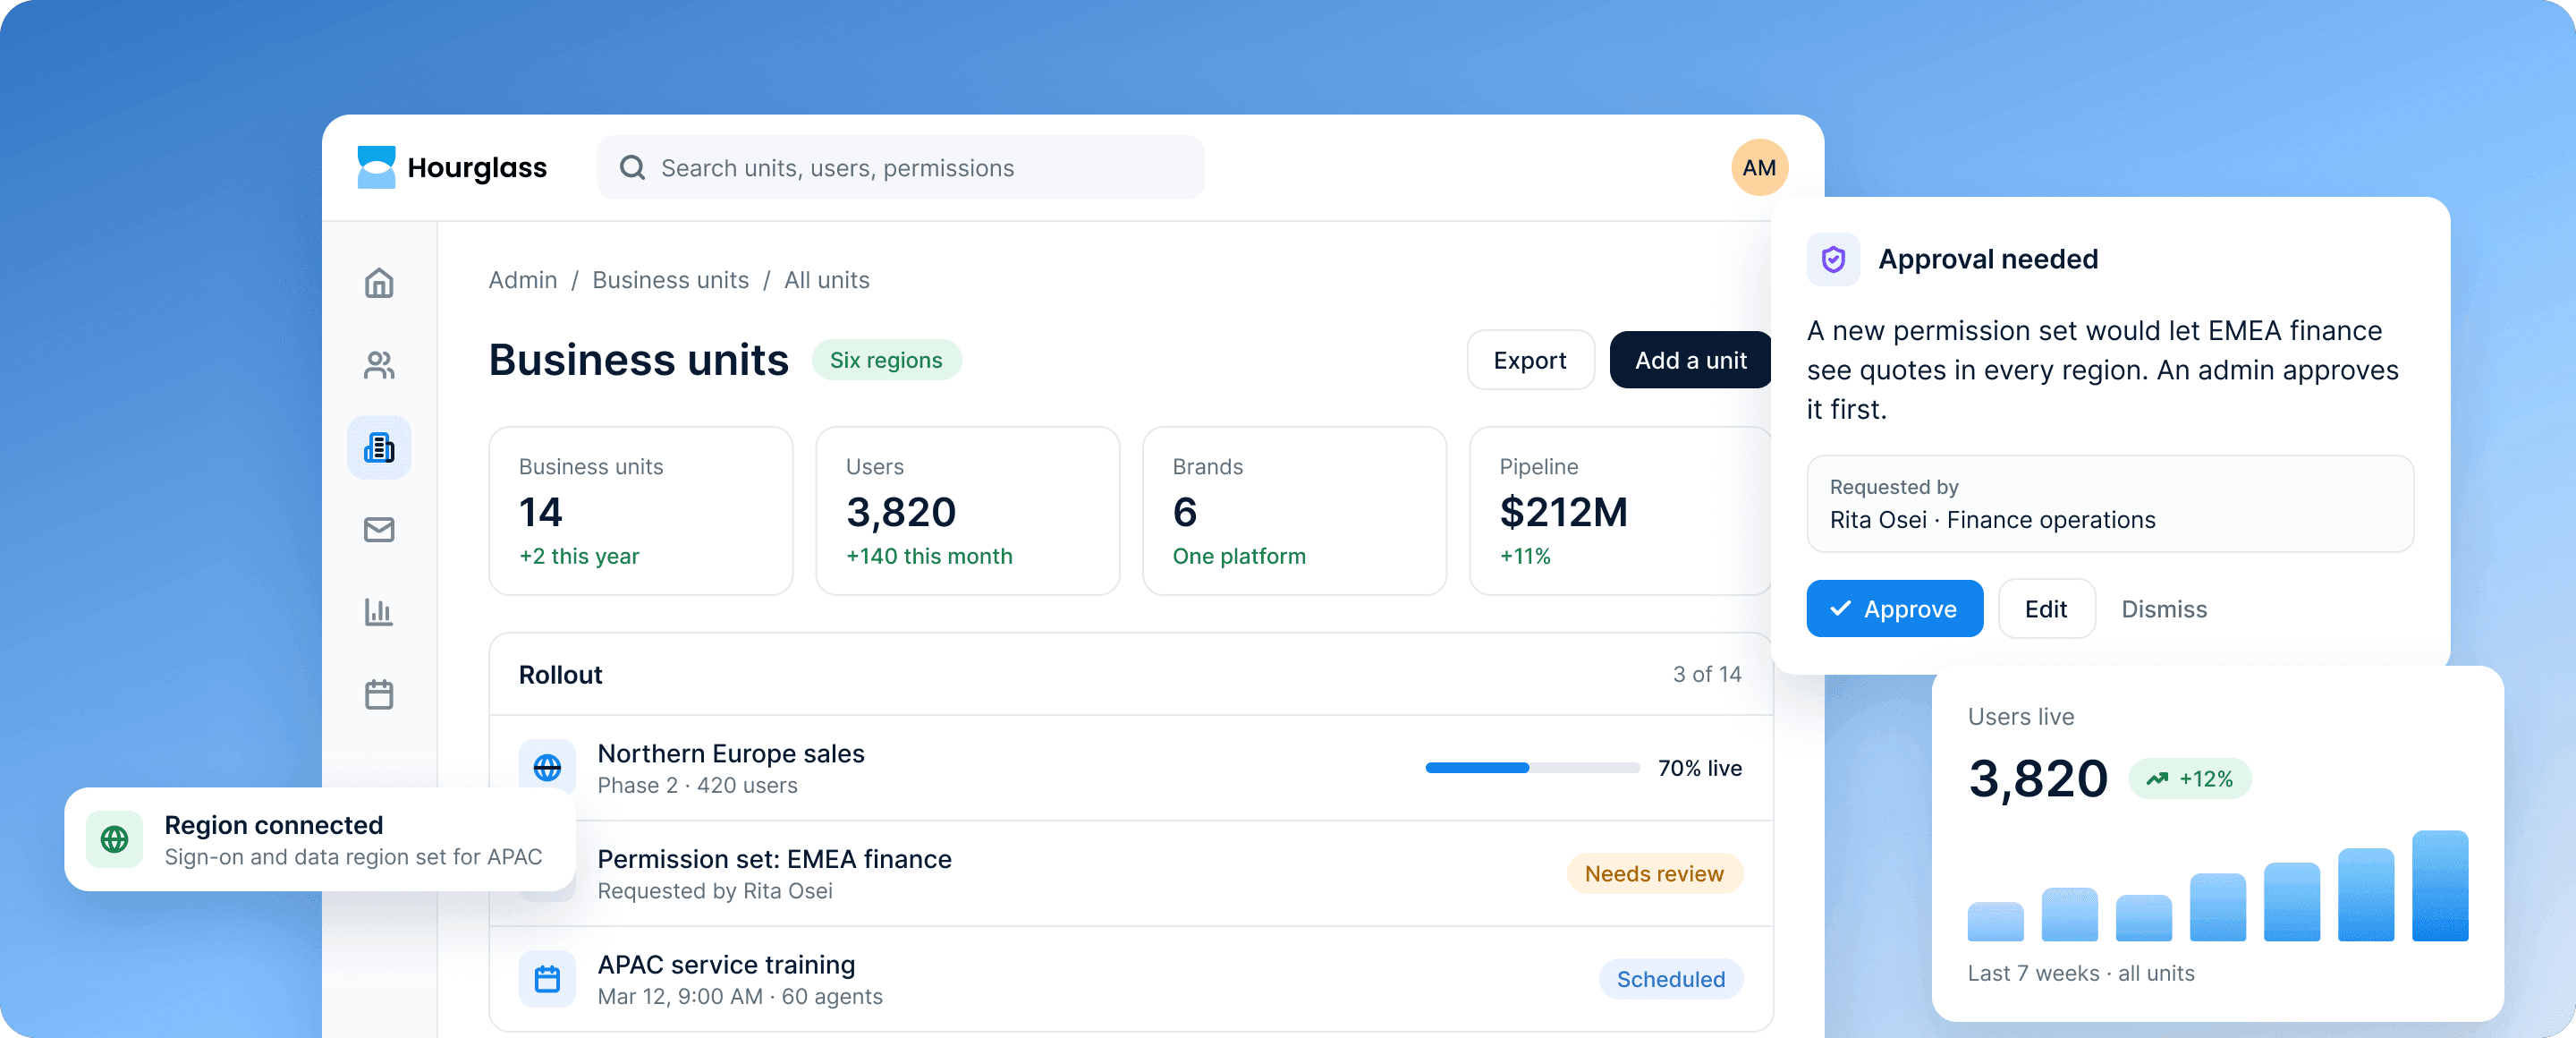
Hourglass runs many brands, regions and business units on one platform, with the controls, permissions and support large organizations need.

Hourglass admin for many business units: 14 units, 3,820 users and six brands, beside a new permission set waiting for an admin's approval.
2 · From Hourglass for enterprises (opens in a new tab)
Enterprise

Built to run across the whole organization

One platform for every team, set up the way each one works.

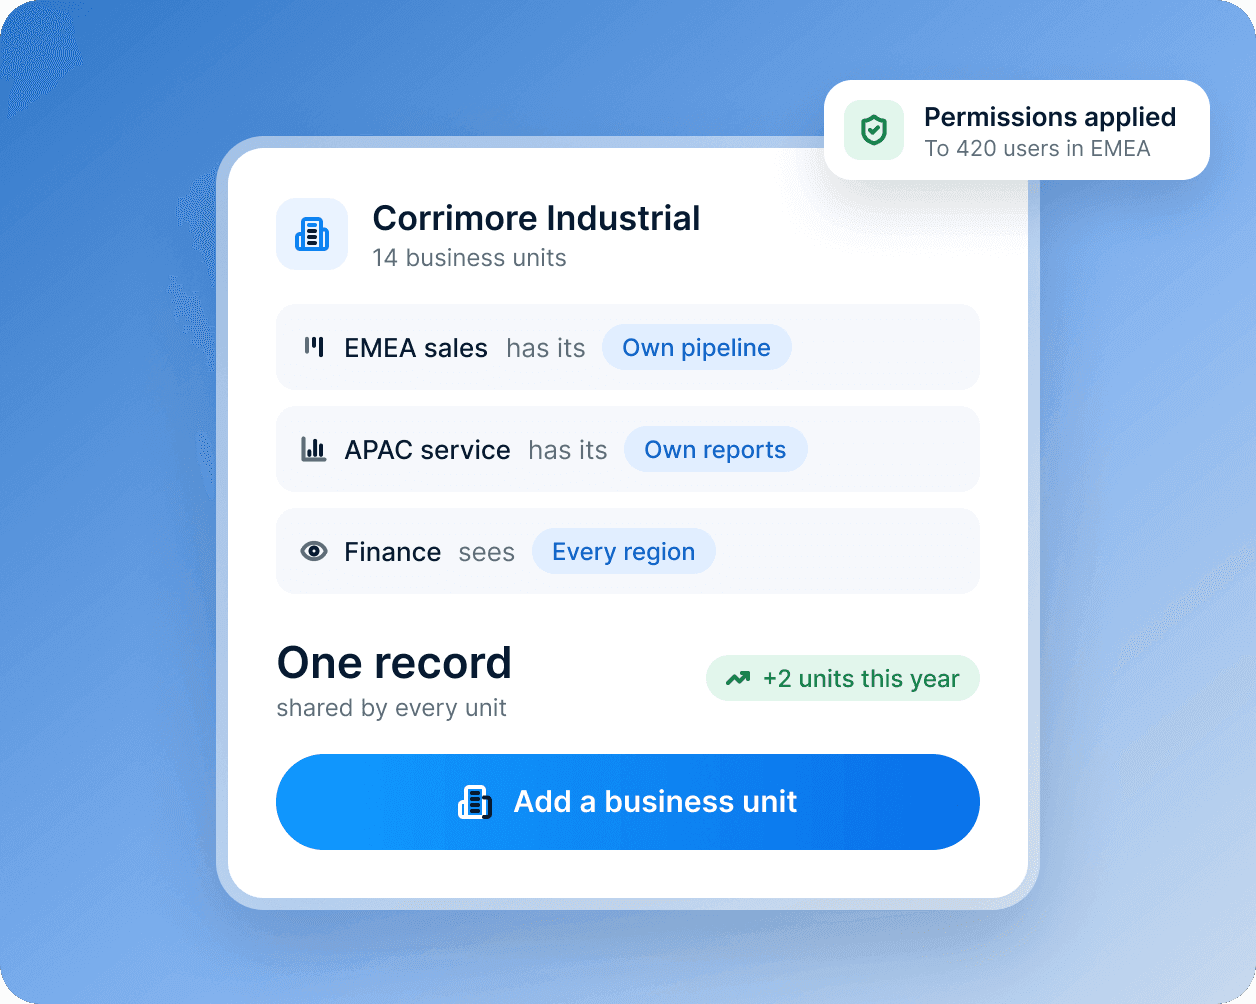
A company with 14 business units: each with its own pipeline and reports, and finance seeing every region.

Many teams, one platform

Give each brand, region or business unit its own pipelines, permissions and reports, while leadership sees the whole picture.

  • Pipelines, permissions and reports per unit
  • One customer record for every unit
  • Leadership sees the whole picture
Learn more about security and control
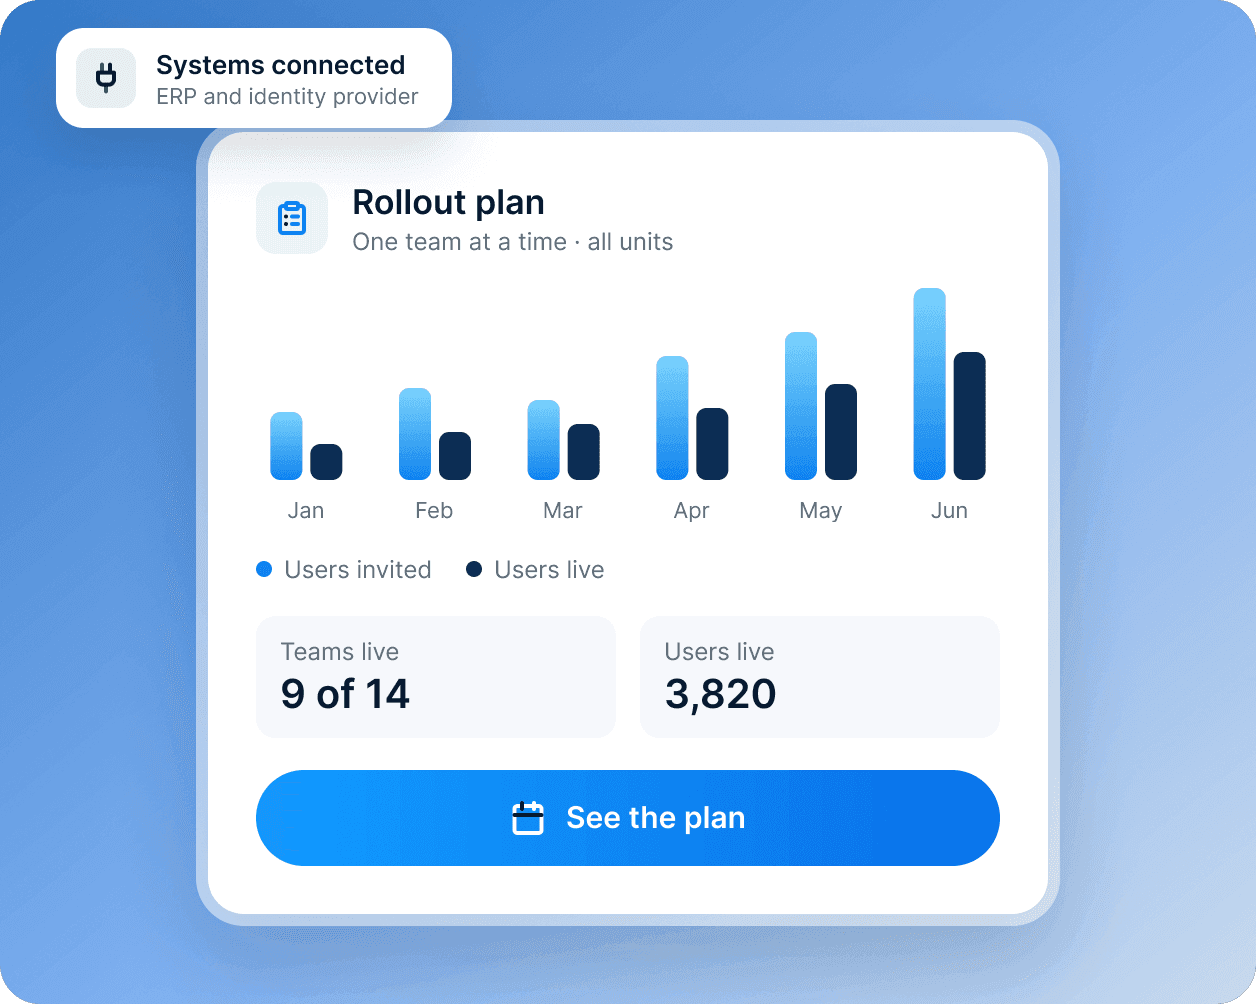
A rollout plan across business units: users invited and live, nine of 14 teams live, with systems connected.

A rollout planned with you

Our onboarding team plans the rollout with you, connects your systems and trains your people, one team at a time.

  • A plan made with our onboarding team
  • Your systems connected for you
  • Training for each team as it moves
Learn more about talking to our team
3 · On 2 site pages, such as Hourglass for enterprises (opens in a new tab)
Security and control

Security and control, built into every hub

The controls your IT, security and compliance teams ask for first.

  • Field-level permissions

    Decide who can see and edit each field, by role and team.

  • Audit history

    Every change and agent action, with who did it and when.

  • Approval steps

    Require a person’s sign-off before agents send or change anything you choose.

  • Single sign-on

    Sign in with SAML or OpenID Connect, provision users with SCIM, and require two-step login.

  • Data region choice

    Choose where your customer data is stored.

  • Encryption

    Data encrypted in transit and at rest.

DocsFrom the Hourglass documentation

The rest of your answer, from the docs

The site doesn't have a page for this yet, so here is the documentation, word for word.

Administration › Security › User provisioning (SCIM)

Turn on SCIM

On Enterprise, open Settings › Security › Provisioning and select Generate token. The token is shown once; store it in your identity provider with the base URL https://api.hourglass.app/scim/v2.

From then on, users and groups assigned to the Hourglass app are created and updated automatically.

Read the full guide in the docs (opens in a new tab)

Administration › Security › User provisioning (SCIM)

Attribute mapping

userName maps to the person's email, and name.givenName and name.familyName to their name. Groups in your identity provider map to Hourglass teams, and you choose a role per group, so moving someone between groups moves them between teams.

Read the full guide in the docs (opens in a new tab)

Administration › Security › User provisioning (SCIM)

Deprovisioning

When a user is deactivated or unassigned in your identity provider, Hourglass suspends them within 5 minutes: they're signed out and can't sign in. Their open deals, tickets and tasks move to their manager, and their records keep their history. An admin can delete the user later; suspension frees the seat straight away.

Read the full guide in the docs (opens in a new tab)